
Overview
Application security services in modern enterprises must do more than protect code—they must enable secure innovation at speed. As digital platforms scale, every application becomes a potential entry point. We help teams embed security across the software lifecycle, aligning with DevOps, satisfying compliance mandates, and reducing real-world risk.
Our approach integrates seamlessly into how your teams already build. From threat modeling and secure design to runtime monitoring and remediation guidance, we provide the structure and tools to shift left, respond fast, and scale safely. We don’t treat security as a final step. We help you build secure-by-default applications, improve collaboration between security and development, and reduce friction between release velocity and protection.
With deep experience across finance, healthcare, retail, and government platforms, we’ve helped global organizations standardize secure coding practices, reduce vulnerabilities, and improve audit-readiness without compromising performance.

Services
Core Application Security Services That We Offer:
Secure Software Development Lifecycle (SDLC)
- Threat modeling at design phase using STRIDE and DREAD frameworks
- Security acceptance criteria embedded into Agile stories
- CI/CD pipeline integration with security gates
- Developer enablement programs with real-world exploit scenarios
Static and Dynamic Application Testing
- SAST and DAST with contextual results for triaged remediation
- IAST for deep runtime insights in test environments
- Pipeline-integrated scanning with SLAs and false-positive reduction
- Real-time dashboards for AppSec posture monitoring
Secure Architecture and Threat Modeling
- Architecture reviews for monolith, microservices, and serverless
- OWASP Top 10, CWE/SANS, and MITRE ATT&CK mapping
- Pattern libraries for secure API design and encryption enforcement
- Proactive design remediation support for critical applications
DevSecOps Enablement
- Security integrated into Git workflows and CI tools like GitHub Actions, Jenkins, Azure DevOps
- Infrastructure as code (IaC) scanning and policy enforcement
- Container and Kubernetes pipeline security (image signing, vulnerability scans)
- Shift-left playbooks aligned to your developer toolchain
Software Composition Analysis (SCA)
- Open-source package scanning with license and version control
- CVE detection, SBOM (Software Bill of Materials), and alerting
- Auto-patching and upgrade recommendations for critical dependencies
- Centralized view of third-party risk across repositories
Recognized for Building Secure Applications at Scale
Consistently trusted for secure SDLC practices, automated vulnerability management, and measurable risk reduction across modern platforms.
Secure Code. Trusted Processes. Audit-Ready Assurance.
Enterprise application security needs to be both effective and defensible. We build security into every stage of your development lifecycle, while maintaining full traceability for internal controls, external audits, and regulatory mandates.
Regulatory Mapping and Policy Alignment
We align your AppSec program with ISO 27001, SOC 2, PCI-DSS, HIPAA, GDPR, and industry-specific controls.
Security Validation at Scale
Standardized vulnerability management, patch SLAs, and risk scoring tied to business impact — not just severity.
Code-to-Cloud Traceability
From initial commit to runtime monitoring, we deliver full security coverage across build, test, release, and operations.
Scalable, Repeatable, Documented
We help enterprise teams create security blueprints, playbooks, and documentation that scale across global delivery centers and audit cycles.
Success Stories
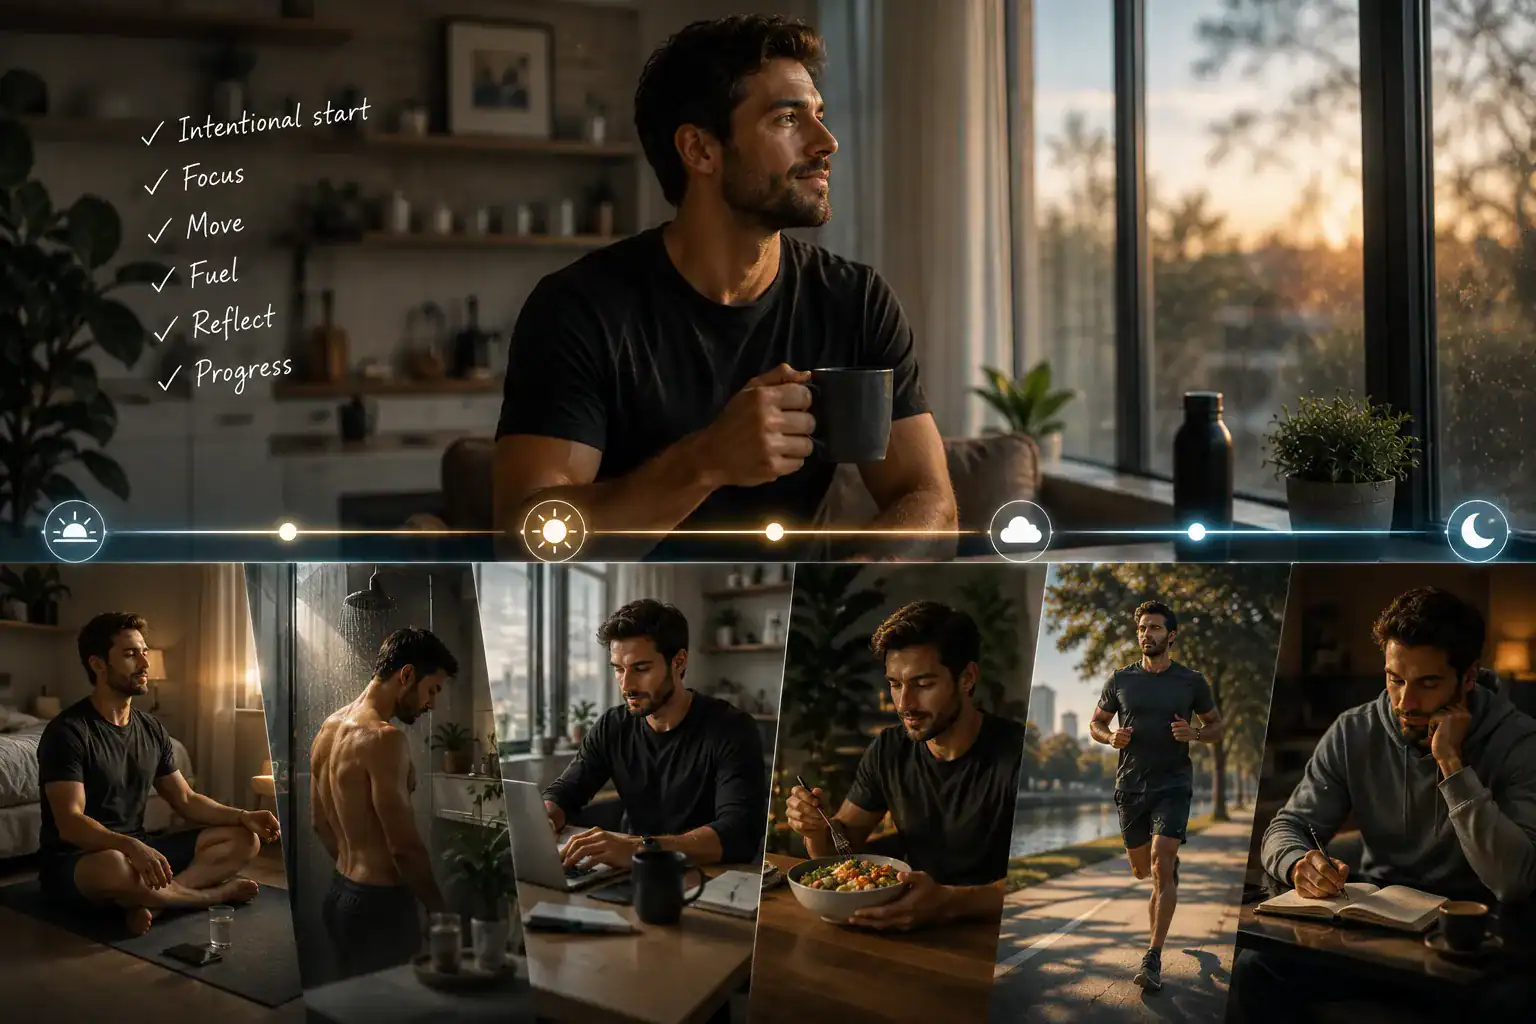
Designing Panbit Into a Mobile Habit Platform Built on Commitment Psychology and Social Accountability
See how Zazz built Panbit, a psychology-driven habit-building platform powered by commitment locks, reinforcement systems, and real social accountability.
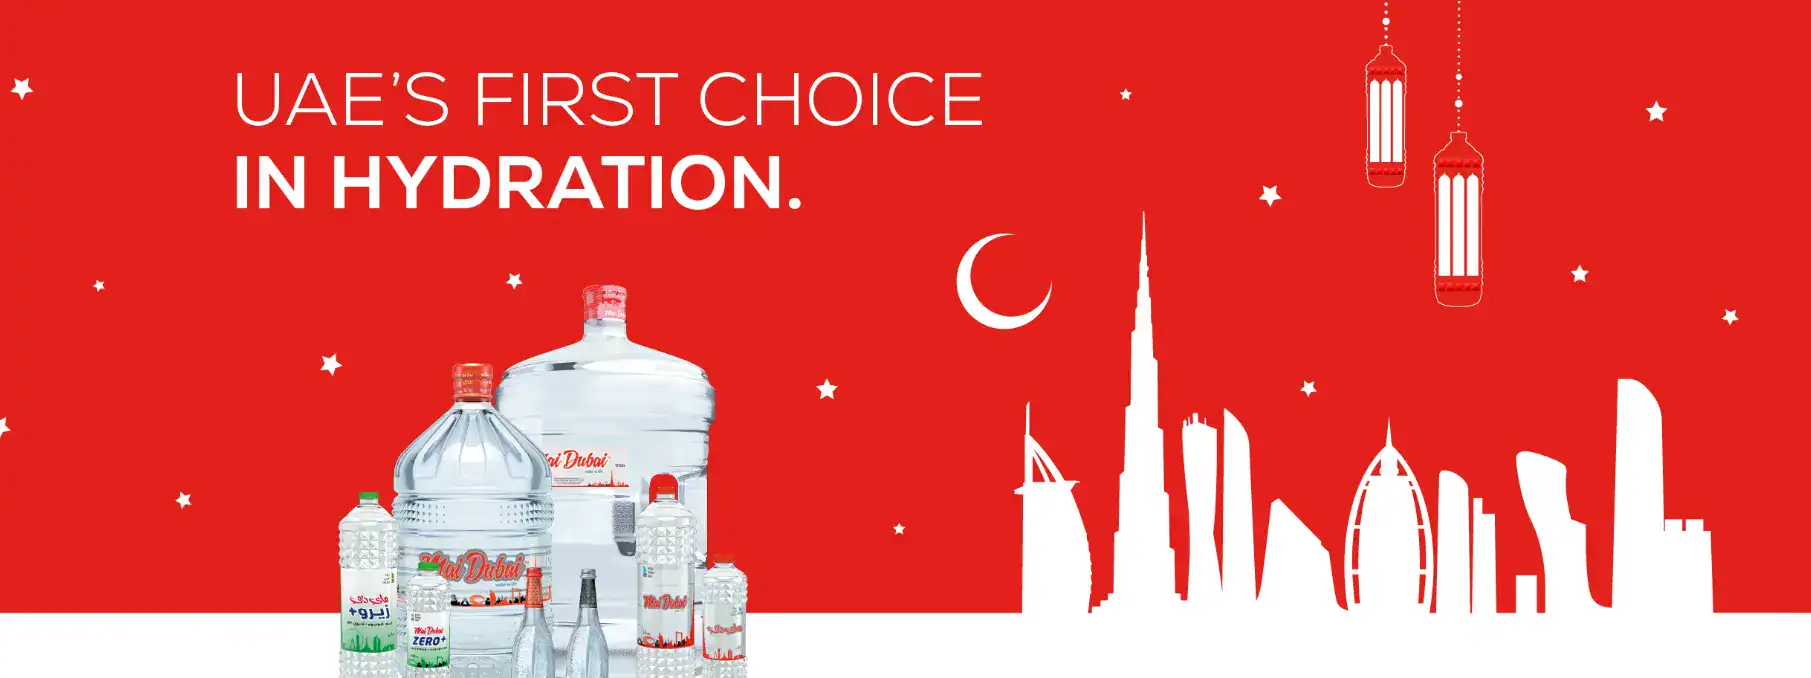
Redefining Digital Commerce for a Market-Leading Beverage Brand
Mai Dubai Water: Building a Scalable Digital Foundation for a Market-Leading Beverage Brand
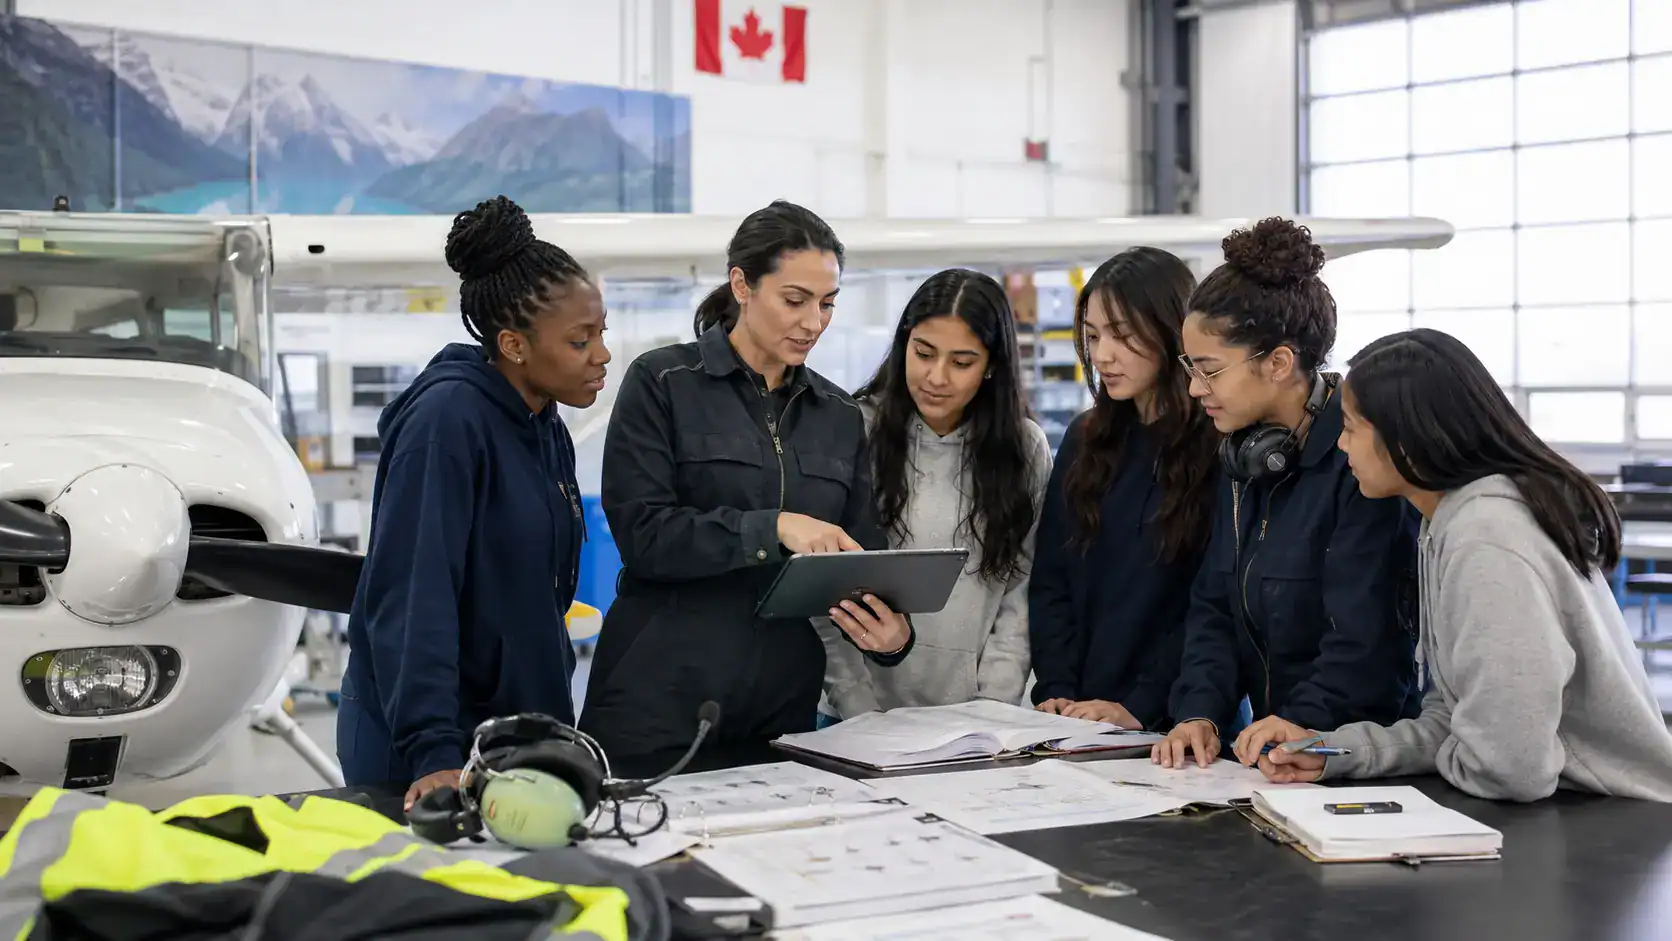
Building a National Digital Ecosystem for Aviation Workforce Development Across Canada
Building a National Digital Ecosystem for Aviation Workforce Development Across Canada
Secure Innovation at Enterprise Scale
Our clients don’t slow down for security. They move faster — with less risk and more confidence.
Talk to an Application Security AdvisorReduction in production vulnerabilities after SDLC security integration
Faster remediation cycles with in-pipeline AppSec feedback loops
Audit success rate when mapped to SOC 2 and ISO controls
How We Deliver Value – In Our Client’s Words
Frequently Asked Questions
We align AppSec controls to Agile sprints, CI/CD pipelines, and tooling — without interrupting your delivery rhythm. Security gates, automated scans, and policy checks happen in parallel with development.
Yes. We assess current state, identify gaps, benchmark against industry standards, and define a roadmap with measurable milestones.
We secure web apps, APIs, mobile apps, internal tools, customer platforms, and cloud-native microservices — across monoliths and distributed architectures.
Absolutely. We establish governance models and shared AppSec tooling for all delivery partners — including external vendors and offshore teams.
Yes. We offer custom secure coding programs, OWASP training, and threat modeling workshops tailored to your stack and development language.
We deliver detailed dashboards, risk scoring, vulnerability trends, compliance coverage maps, and executive-level summaries with remediation priorities.
Build Software That’s Secure by Design
Security doesn’t have to slow you down. We help you integrate it into how your teams work, from planning to production.
Schedule an Application Security Consultation
Talk to Our Application Security Team
Contact now

Scale Application Security Across Your Environments
Make AppSec an accelerator, not an afterthought.