
CrowdStrike Falcon Services
CrowdStrike Falcon Services | 24/7 EDR, Fully Deployed and Managed, Behavioral Detection
Zazz delivers end-to-end CrowdStrike Falcon services for businesses that require advanced endpoint protection without building an internal security operation. We manage everything from Falcon sensor deployment and host group configuration to prevention policy tuning, alert investigation, and real-time incident response so your organization stays protected every hour of every day.
Fill Out the Form to Request a CrowdStrike Falcon Security Assessment
We only use your info to contact you about your IT needs.
Full Lifecycle CrowdStrike Falcon Services for Your Business:
CrowdStrike Falcon Sensor Deployment and Rollout
- Deploy sensors across Windows, macOS, Linux using GPO, Intune, JAMF or custom tools
- Configure CID, tokens, and grouping for proper environment segmentation
- Ensure full endpoint coverage before monitoring starts
Prevention Policy Configuration and NGAV Management
- Configure ML-based prevention, ransomware protection, exploit mitigation
- Tune detection and prevention sensitivity to balance security and false positives
- Manage exclusions for legitimate apps without weakening protection
Endpoint Detection and Response (EDR) Management
- Set up detection policies with custom IOAs and behavioral rules
- Apply policies across host groups based on system criticality
- Continuously triage alerts and escalate real threats
Real-Time Response (RTR) Threat Investigation and Containment
- Investigate live endpoints including processes, registry, network activity
- Isolate hosts, kill processes, remove malicious files remotely
- Provide detailed incident reports with root cause and remediation
Custom IOA and IOC Rule Management
- Create IOAs tailored to your environment and threat landscape
- Block malicious hashes, IPs, domains using IOC management
- Regularly clean up outdated rules to reduce noise
Falcon Fusion SOAR Workflow Automation
- Automate response actions based on detection triggers
- Integrate with SIEM, ITSM, and communication tools
- Maintain playbooks to keep automation accurate and scalable
Struggling to Get Real Value From Your CrowdStrike Falcon Investment?
- We deployed CrowdStrike Falcon across our endpoints but the prevention and detection policies are still running on default settings from initial installation.
- Our Falcon console generates detections that nobody has the time or expertise to investigate, so most of them go unreviewed and unacted upon.
- We currently do not have sufficient visibility into which endpoints have active Falcon sensors and which do not, leaving potential coverage gaps that we are unable to accurately quantify.
- Our IT team installed Falcon but has never configured host groups, policy precedence, or custom IOA rules, so the platform is significantly underutilized.
- We have Falcon Spotlight enabled but no structured process for prioritizing CVEs or tracking patch remediation progress against real exploitation risk.
- When Falcon detects something on one of our systems, our team has no clear process for investigating it through RTR or determining the actual scope.
- We are not confident our Falcon exclusions are configured correctly, and we suspect we may have created gaps that allow malicious files to pass through.
- Our organization has multiple endpoint types across Windows, macOS, and Linux but Falcon policies are only configured for our primary Windows environment.
If your Falcon deployment feels incomplete or difficult to manage, you are not alone. Zazz provides the operational maturity, tuning, and response capability required to make Falcon work as intended.
Book a Free Consultation
We evaluate your Falcon setup end to end, identify underutilized capabilities and risk areas, and show how our managed services can turn Falcon into a fully operational security layer.
How Zazz Outperforms Other CrowdStrike Falcon Service Providers:
Security Capability
Sensor Deployment
Prevention Policy Configuration
EDR Detection Depth
Alert Triage and Investigation
Incident Response Speed
Vulnerability Management
Zazz
Structured rollout across all OS types with validated 100% coverage before monitoring begins
ML sliders, script controls, and behavioral prevention configured beyond factory defaults
Custom IOA rules, host group policies, and behavioral triggers aligned to your threat model
Every Falcon detection reviewed by specialists with RTR investigation for confirmed threats
Immediate RTR-based containment and forensic investigation by a dedicated response team
Falcon Spotlight CVEs prioritized by exploitation risk and actioned through a structured process
Other Vendors
Partial deployment with uncovered endpoints creating invisible gaps in detection scope
Default policies left unchanged, missing organization-specific exclusions and tuning
Standard detection rules only, with no custom IOA development or policy refinement
Detections accumulate unreviewed or are dismissed without proper investigation process
Hours to days without established process, often relying on vendor support queue
Spotlight data visible in dashboard but not actioned or prioritized against real exposure
Sensor Deployment
Zazz
Structured rollout across all OS types with validated 100% coverage before monitoring begins
Other Providers
Partial deployment with uncovered endpoints creating invisible gaps in detection scope
Prevention Policy Configuration
Zazz
ML sliders, script controls, and behavioral prevention configured beyond factory defaults
Other Providers
Default policies left unchanged, missing organization-specific exclusions and tuning
EDR Detection Depth
Zazz
Custom IOA rules, host group policies, and behavioral triggers aligned to your threat model
Other Providers
Standard detection rules only, with no custom IOA development or policy refinement
Alert Triage and Investigation
Zazz
Every Falcon detection reviewed by specialists with RTR investigation for confirmed threats
Other Providers
Detections accumulate unreviewed or are dismissed without proper investigation process
Incident Response Speed
Zazz
Immediate RTR-based containment and forensic investigation by a dedicated response team
Other Providers
Hours to days without established process, often relying on vendor support queue
Vulnerability Management
Zazz
Falcon Spotlight CVEs prioritized by exploitation risk and actioned through a structured process
Other Providers
Spotlight data visible in dashboard but not actioned or prioritized against real exposure
Operational Excellence in Falcon Security Backed by Proven Frameworks
We apply proven security standards and operational rigor to every Falcon deployment we manage. From configuration to response, our approach ensures consistent protection, measurable performance, and audit-ready security operations.
How We Secure Your Business With CrowdStrike Falcon Services
A structured approach to deploying, managing, and optimizing your CrowdStrike Falcon environment end to end
Assess Your Falcon Environment and Identify Gaps
We conduct a structured review of your CrowdStrike Falcon deployment, including sensor coverage, policy configurations, host groups, IOA/IOC rules, Fusion workflows, and detection backlog. This gives a clear view of gaps and areas that need improvement.
Deploy, Configure, and Validate to Production Standard
We complete sensor rollout, configure prevention and detection policies, build custom IOA rules, set up host groups and workflows, and validate full coverage. All changes are tested and aligned to your environment before going live.
Monitor, Respond, and Continuously Optimize
We manage ongoing monitoring, alert triage, RTR investigations, and incident response. We also deliver vulnerability insights, optimize policies over time, and provide structured reporting with direct access to our team.
Recognized for Excellence in CrowdStrike Falcon Management
Zazz is rated by clients for its ability to operationalize CrowdStrike Falcon effectively, ensuring continuous protection, rapid response, and measurable improvements in endpoint security posture.


The Zazz Edge in CrowdStrike Falcon Management:
Specialist-Led Sensor Deployment.
We manage Falcon deployment end to end across all operating systems with platform-specific expertise.
Immediate RTR Response.
Our team performs live investigation and containment using RTR without delays.
100% Coverage Assurance.
We validate full sensor deployment and continuously monitor for coverage gaps or failures.
Multi-OS Environment Expertise.
We manage Falcon across Windows, macOS, and Linux with consistent protection.
Success Stories


Turning Complex Real Estate Workflows into Seamless Mobile Experiences
Zazz partnered with New Western to reimagine their digital product-from fragmented web flows to a mobile-first experience backed by full-stack support.
Driving Local Retail Growth with a High-Performing Mobile App for ViewGem
How Zazz built ViewGem’s mobile app to boost user retention, drive foot traffic, and help retailers promote local offers through a seamless digital platform.
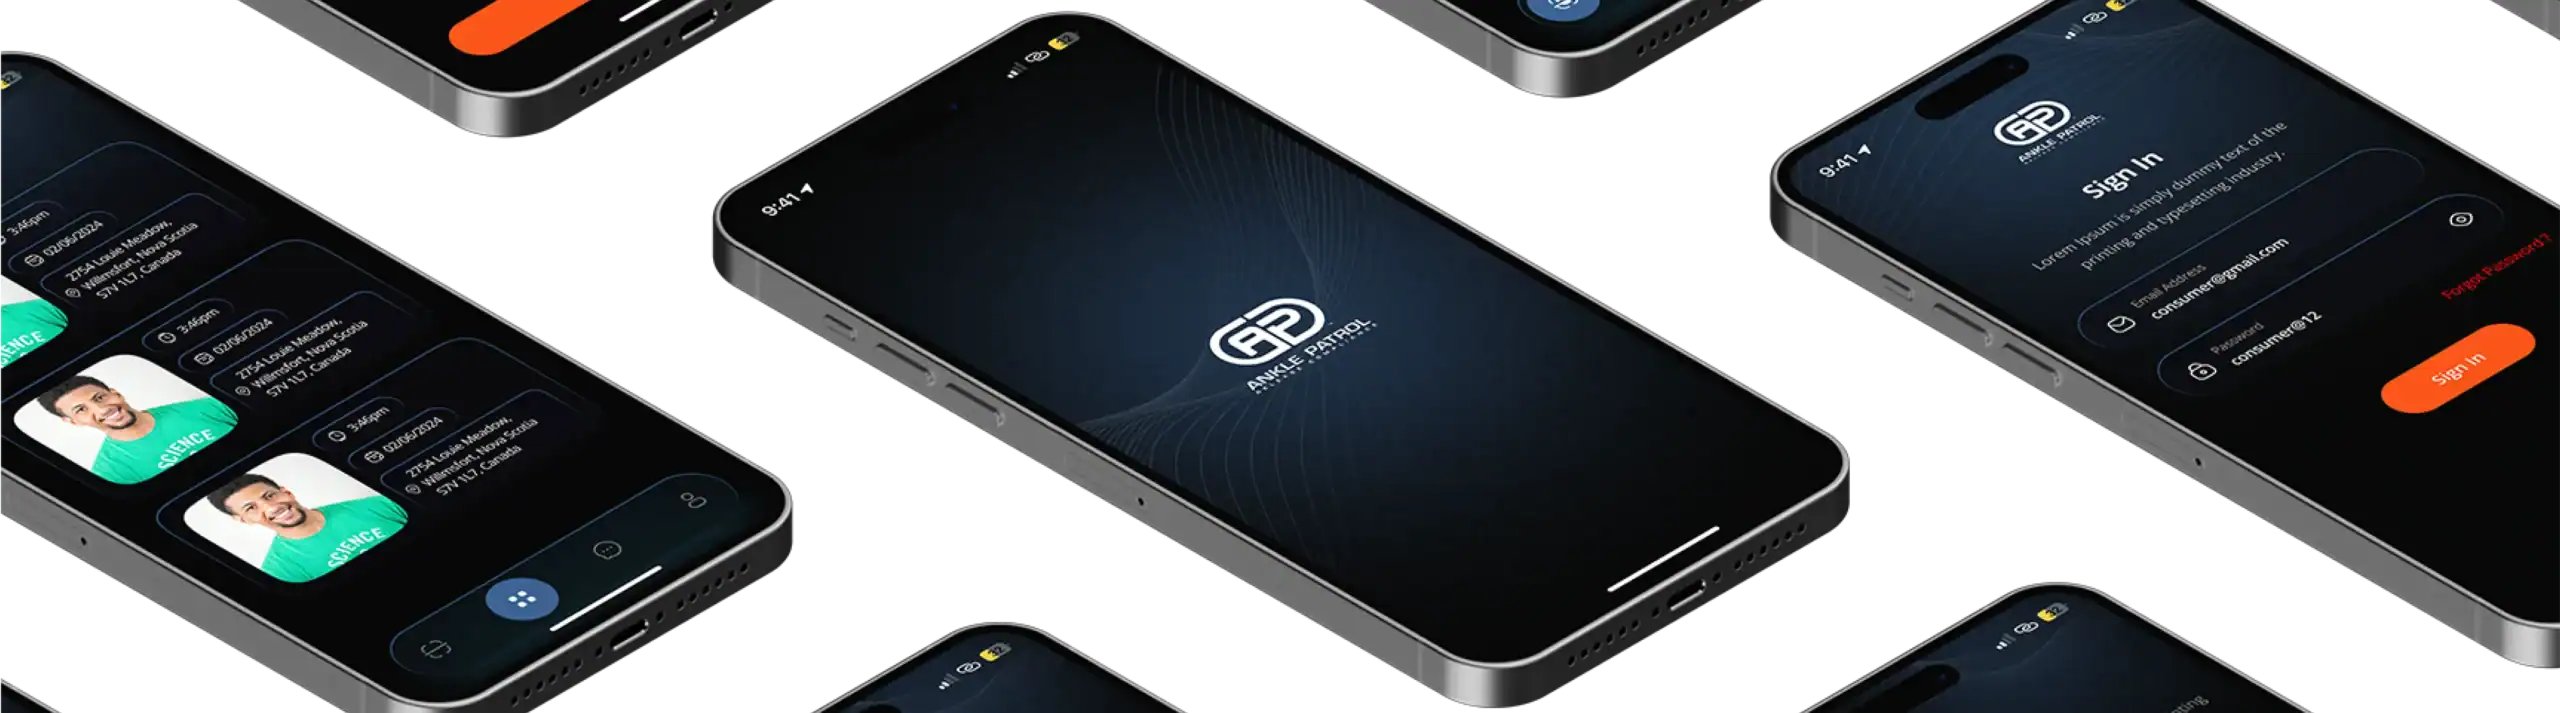
From Manual Compliance to a Secure, Scalable Mobile Platform
Designed, built, and maintained end-to-end, Ankle Patrol is a secure mobile platform that modernised compliance tracking and supervision workflows for the public safety sector.
Articles
Explore All Articles and Reports
What Changes When Falcon Is Fully Managed By Zazz:
Behavioral Threats Identified Before They Escalate Into Business Incidents
CrowdStrike Falcon detects adversary behavior early, before lateral movement or data exfiltration begins. With active management from Zazz, detections are reviewed immediately, threats are contained through RTR, and incidents are resolved before impacting critical systems.
Complete Endpoint Visibility With No Coverage Gaps
Partial sensor deployment creates critical blind spots. Zazz ensures full Falcon coverage across all endpoints, including servers, remote devices, and non-standard environments.
Detection Policies Calibrated to Your Actual Threat Environment
Default Falcon policies are built for general use. Zazz configures prevention and detection policies, including custom IOA rules and tuning, aligned to your specific risk environment.
Faster Incident Response When the Window to Act Is Smallest
The time between compromise and spread is often minutes. With RTR-based investigation and rapid containment, Zazz reduces the scope and impact of incidents before they escalate.
What Effective Falcon Management Looks Like in Numbers
Request a CrowdStrike Falcon ConsultationFaster Detection-to-Response Time After Optimization
Average Time to Stabilize Detection Backlogs
Reduction in False Positives After Policy Tuning
How We Deliver Value in Our Clients’ Words
Frequently Asked Questions
Our services cover the full Falcon lifecycle, including deployment assessment, sensor rollout, policy configuration, custom IOA development, host group setup, Fusion workflows, and Spotlight management. We provide 24/7 monitoring, alert triage, RTR-based investigation, incident response, reporting, and continuous optimization.
Having Falcon deployed is not the same as managing it. Many organizations run default policies, lack custom IOAs, have incomplete coverage, and do not investigate alerts. Zazz brings your environment to a fully managed standard by optimizing configuration, completing coverage, and handling ongoing monitoring and response.
Most deployments are completed within 48 to 72 hours, depending on endpoint volume, OS diversity, and deployment tools. Additional time may be required for policy configuration and custom rule setup. A clear timeline is provided during the initial assessment.
Every detection is reviewed immediately using alert data and behavioral context. We determine if it is a real threat or false positive. For confirmed threats, we initiate RTR investigation, contain the threat, remove malicious artifacts, and deliver a detailed incident report.
Custom IOA rules are behavioral detections tailored to your environment. While Falcon covers common attack techniques, advanced threats can bypass standard rules. Zazz builds IOAs aligned to your applications, industry risks, and threat patterns to improve detection accuracy.
We provide 24/7 monitoring and response. Incidents detected outside business hours are investigated and contained immediately, with notifications sent to your team and full reporting delivered after resolution.
Yes. Managed Falcon environments provide the documentation, detection logs, and response records required by insurers. This supports renewals, improves underwriting outcomes, and aligns with frameworks like NIST, CIS, and ISO 27001.
Falcon support is security-focused, covering detection, response, policy management, and investigation. Standard IT support handles general infrastructure and operations. These are distinct functions requiring different expertise.
We support organizations across industries including the education industry, finance, healthcare, legal, manufacturing, technology, retail, and the construction industry. Falcon is configured with industry-specific threat models to match the risks relevant to your sector.
Zazz supports organizations across their full security and IT technology stack. Alongside our CrowdStrike Falcon services, we provide Huntress support services for businesses needing additional managed endpoint detection layers, Vanta support services for compliance automation and certification management, advanced email security through Mimecast support services, enterprise credential and identity management with 1Password, endpoint and infrastructure management via Ivanti support services, and Cisco Meraki support services for managed network infrastructure. Many of our clients engage Zazz across multiple platforms to maintain consistent expert management across their entire technology and security environment rather than managing each tool independently.
Dedicated CrowdStrike Falcon Services for Organizations That Cannot Afford Endpoint Gaps
Our CrowdStrike Falcon managed services combine expert deployment, continuous detection management, rapid RTR response, and structured reporting. Your environment is handled by a dedicated team that understands your setup and responds to threats with speed and precision.
Get CrowdStrike Falcon Services
Request a Consultation
Fill out the form to assess your Falcon setup and learn how to strengthen detection, response, and overall endpoint security.
Contact now

Turn CrowdStrike Falcon Into a Fully Operational Defense Layer
Whether your Falcon environment is newly deployed or long overdue for optimization, Zazz provides the expertise to close gaps, improve detection, and ensure continuous protection.