
Terraform Services
Terraform Services | Infrastructure Control, State Management, and Execution Governance
Zazz delivers Terraform services to structure infrastructure as code, manage state reliably, and enforce controlled execution across environments. We ensure infrastructure changes are predictable, auditable, and aligned with operational requirements.
Fill the form to Bring Control to Your Infrastructure as Code
We only use your info to contact you about your IT needs.
Our Terraform Services
Terraform Implementation
- Structured setup of infrastructure as code across environments
- Standardized module and workspace design
- Alignment with deployment and operational workflows
Terraform Configuration Management
- Structured setup of infrastructure as code across environments
- Standardized module and workspace design
- Alignment with deployment and operational workflows
Terraform Management
- Ongoing oversight of infrastructure state and execution
- Controlled planning and apply workflows
- Continuous refinement of infrastructure definitions
Terraform IAM and Access Control
- Role-based access to infrastructure workflows
- Controlled execution permissions across teams
- Secure handling of credentials and state access
Terraform Support
- Resolution of state conflicts and execution issues
- Optimization of modules and configurations
- Continuous alignment with infrastructure changes
Terraform Partner Services
- Guidance from an experienced Datadog partner
- Advisory on observability architecture and scaling
- Best practices for long-term monitoring strategy
Is this Where Your Terraform Practices Break Down?
- Terraform adopted across teams without a consistent module or workspace structure
- State files stored locally or without proper locking, creating conflict and corruption risk
- IAM policies for infrastructure provisioning over-permissioned and undocumented
- CI/CD integration absent, with infrastructure changes applied manually outside version control
- Module library developed ad hoc with no versioning, testing, or documentation standards
- Drift between declared infrastructure state and actual cloud environment undetected
- Terraform Cloud or Enterprise configured without Sentinel policies or governance enforcement
- No ownership model for ongoing provider updates, module maintenance, or state hygiene
Zazz addresses these challenges by structuring Terraform services around control, consistency, and governed execution.
Book a Free Consultation
Review your infrastructure setup, identify gaps in control, and align Terraform workflows with your operational requirements.
Zazz vs Traditional Terraform Support Approaches
Criteria
State Management Discipline
Execution Governance
Module Standardization
Access and Permissions
Continuous Optimization
Zazz
Structured state handling with clear ownership and control
Controlled plan and apply workflows with defined approvals
Reusable, versioned modules across environments
Role-based access aligned with responsibilities
Infrastructure code refined based on changes and usage
Other Vendors
State managed inconsistently across teams
Uncontrolled execution leading to risk
Ad-hoc module usage with inconsistencies
Broad or unclear access permissions
Static configurations with minimal updates
State Management Discipline
Zazz
Structured state handling with clear ownership and control
Other Vendors
State managed inconsistently across teams
Execution Governance
Zazz
Controlled plan and apply workflows with defined approvals
Other Vendors
Uncontrolled execution leading to risk
Module Standardization
Zazz
Reusable, versioned modules across environments
Other Vendors
Ad-hoc module usage with inconsistencies
Access and Permissions
Zazz
Role-based access aligned with responsibilities
Other Vendors
Broad or unclear access permissions
Continuous Optimization
Zazz
Infrastructure code refined based on changes and usage
Other Vendors
Static configurations with minimal updates
Security and Governance Across Your Terraform Environment
Zazz configures Terraform with least privilege IAM, encrypted state backends, and Sentinel policy enforcement, with every decision documented for audit readiness.
Recognised for Consistent Terraform Service Delivery
A service-led approach focused on control, consistency, and reliable execution of infrastructure changes.
Define Structure and Ownership
We establish module standards, state ownership, and execution boundaries across environments.
Govern Execution and Access
We implement controlled workflows, approvals, and access controls for infrastructure changes.
Maintain and Evolve Continuously
We refine infrastructure definitions based on system changes and operational needs.
Recognised for Consistent Terraform Service Delivery
Zazz is recognised across independent B2B platforms for consistent enterprise infrastructure and DevOps services delivery, assessed on IaC quality and governance outcomes.


Execution Model Behind Zazz’s Infrastructure as Code Services
Alignment with Deployment Workflows
Infrastructure changes are structured to align with release cycles and operational processes.
Ownership of Infrastructure State and Execution
We manage state integrity, execution control, and infrastructure consistency across environments.
Consistent Experience Across Teams
All teams operate within a unified infrastructure framework, reducing inconsistencies and errors.
Continuous Adaptation to Infrastructure Changes
Infrastructure definitions evolve alongside system and architecture changes.
Success Stories


Powering Digital Collectibles—DCT’s Transformation of Community with Scalable, Intelligent Mobile Technology
End-to-End Application Innovation, Embedded Agile Delivery, and Advanced Visual Intelligence for a Leading Hot Wheels Collector Platform


Empowering Torstar Corporation With Specialized Talent To Accelerate Delivery
Empowering Torstar Corporation’s in-house team with specialized mobile talent to accelerate delivery without the overhead of full-time hiring.
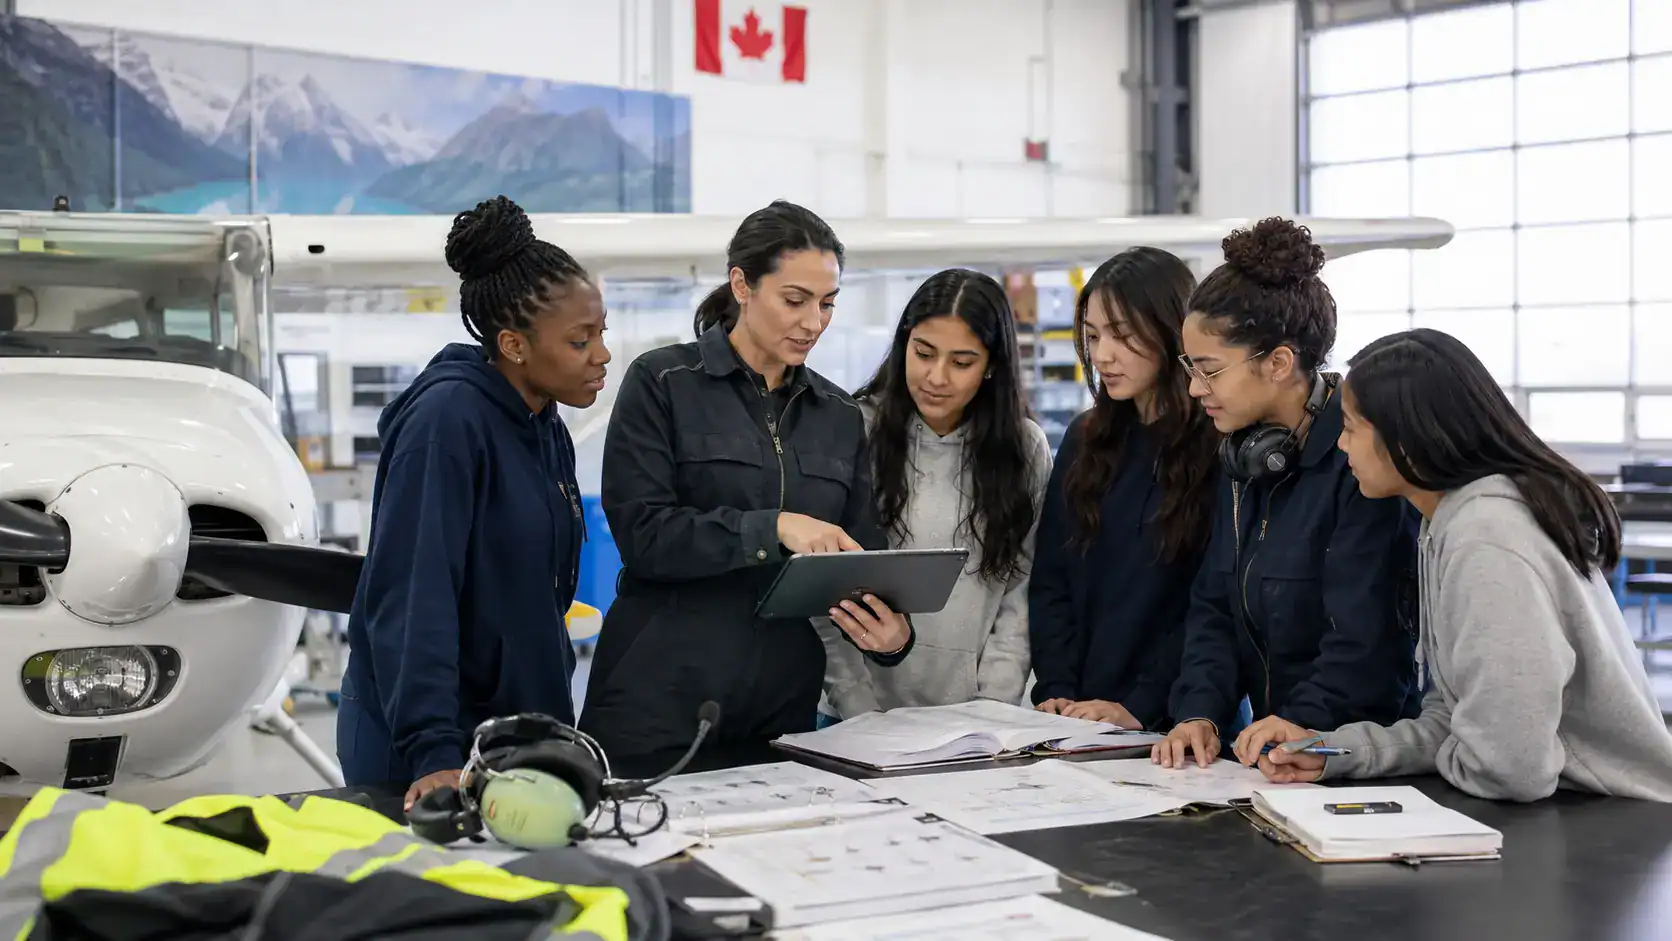
Building a National Digital Ecosystem for Aviation Workforce Development Across Canada
Building a National Digital Ecosystem for Aviation Workforce Development Across Canada
Articles
Explore All Articles and Reports
How Zazz Structures Terraform for Long-Term Stability
Infrastructure Modeled Around Real Environments
We design infrastructure code to reflect actual system architecture and dependencies.
Built-In Control Over Infrastructure Changes
Every change is governed, traceable, and aligned with defined workflows.
Separation of Environments and Responsibilities
Clear boundaries between environments and teams reduce risk and complexity.
Designed for Scale Without Rework
Infrastructure frameworks expand without requiring redesign as systems grow.
Faster Infrastructure Deployment Cycles
Request Terraform Support ServicesReduction in Configuration Drift
Faster Infrastructure Deployment Cycles
Minute Plan Validation Time
How We Deliver Value in Our Clients’ Words
Frequently Asked Questions
Zazz enforces structured workflows, approval gates, and state control to ensure every infrastructure change is predictable and traceable.
We manage state integrity, resolve execution issues, optimize modules, and continuously refine infrastructure definitions as systems evolve.
We standardize modules, enforce version control, and regularly validate infrastructure against declared configurations.
Zazz ensures centralized state handling, controlled access, and locking mechanisms to prevent conflicts and maintain consistency.
We define clear execution boundaries, access controls, and workflows so teams can operate independently without causing conflicts.
We implement controlled plan and apply processes, validate changes before execution, and monitor outcomes to ensure consistency.
We design modular, versioned configurations that can be reused across environments while maintaining consistency and flexibility.
We enforce access controls, execution policies, and auditability within infrastructure workflows to align with governance requirements.
Zazz continuously updates infrastructure code based on architecture changes, scaling needs, and operational feedback.
By automating infrastructure changes and standardizing workflows, we reduce manual intervention and improve efficiency.
Zazz supports platforms including NinjaOne, SentinelOne, ServiceNow, Microsoft 365, Datto, Sophos, and other infrastructure and security systems.
Bring Control to Infrastructure Changes
Zazz ensures infrastructure changes are structured, governed, and predictable.
Request Terraform Support Services
Request a Consultation
Connect with our team to structure your Terraform environment for controlled execution and consistent infrastructure management.
Contact now

Move from Scripts to Managed Infrastructure as Code
Zazz transforms infrastructure automation into a controlled, scalable operational system.